

[Sep 09, 2021] Get Free Updates Up to 365 days On Developing C1000-018 Braindumps
Best Quality IBM C1000-018 Exam Questions
NEW QUESTION 10
An analyst notices that there are a number of invalid Offenses being created from a network node. This node has been determined to be in Domain 2 and has the following log sources sending it events: (3Com 8800 Series Switch from 172.18.1.1, Cisco ACE Firewall from 172.18.1.2, FireEye from 172.18.1.3, and Palo Alto PA Series from 172.18.1.8).
The analyst should create a False Positive Building Block that has a filter:
- A. "when the remote IP is one of the following 172.18.1.1, 172.18.1.2. 1.3 172. 18.18.1.8
- B. "when the destination IP is in 172.18.0.0/16"
- C. "when the local network is Domain 2 and when the source IP is in 172.18.0.0/16"
- D. "when the local network is Domain 2 and when the source IP is in 172.18.0.0/16"
Answer: D
NEW QUESTION 11
An analyst is investigating access to sensitive data on a Linux system. Data is accessible from the /secret directory and can be viewed using the 'sudo oaf command. The specific file /secret/file_08-txt was known to be accessed in this way. After searching in the Log Activity Tab, the following results are shown.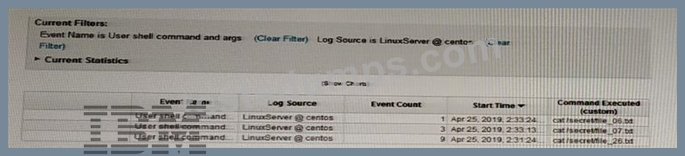
When interpreting this, the analyst is having trouble locating events which show when the file was accessed.
Why could this be?
- A. The 'LinuxServer @ cantos' log source has boon configured as a Faise Positive and the specific event for that file has been dropped.
- B. The 'LinuxServer @ centos' log source has coalescing configured and the specific event for that file can only be accessed by clicking on the 'Event Count' value.
- C. The 'LinuxServer @ centos' log source has not been configured to send the relevant events to QRadar.
- D. The ;LinuxServer @ centos; log source has coalesscing conigured and the specific event for that file has been discardedd.
Answer: B
NEW QUESTION 12
An analyst needs to investigate an Offense and navigates to the attached rule(s).
Where in the rule details would the analyst investigate the reason for why the rule was triggered?
- A. Rule responses
- B. Rule actions
- C. List of test conditions
- D. Rules response limiter
Answer: A
NEW QUESTION 13
Which graph types are available for QRadar SIEM reports? (Choose two)
- A. Histogram
- B. Pie
- C. Stacked Bar
- D. Frequency curve
- E. Trivial curve
Answer: B,C
Explanation:
Explanation
https://www.ibm.com/docs/en/qsip/7.4?topic=management-graph-types
NEW QUESTION 14
An analyst needs to find all events that are creating offenses that are triggered by rules that contain the word suspicious in the rule name.
Which query can the analyst use as a working sample?
- A. SELECT LOGGEDOFFENSE(logsourceid), * from offense_events where RULENAME(creeventlist) ILIKE ,%suspicious%'
- B. SELECT LOGSOURCERULES(logsourceid), " from rule_events where RULENAME(creeventlist) ILIKE '%suspicious%'
- C. SELECT LOGSOURCETYPE(logsourceid), - from log_events where RULENAME(creeventlist) ILIKE '%suspicious%'
- D. SELECT LOGSOURCENAME(logsourceid), * from events where RULENAME(creeventlist) ILIKE
,o/0suspicious%'
Answer: D
NEW QUESTION 15
Where can an analyst investigate a security incident to determine the root cause of an issue, and then work to resolve it?
- A. Network Activity tab
- B. Risk tab
- C. Offense tab
- D. Vulnerabilities tab
Answer: D
NEW QUESTION 16
An analyst has been asked to present a report of all the incidents that have been detected by QRadar in the last
24 hours.
How can the analyst achieve this?
- A. Create a Common saved search from the last 24 hours and then using the Reports tab, create a report to make use of the existing saved search.
- B. Create an Event saved search from the last 24 hours and then using the Reports tab, create a report to make use of the existing saved search.
- C. Create an Offense saved search from the last 24 hours and then using the Reports tab, create a report to make use of the existing saved search.
- D. Create an Event saved search from the last 24 hours and then using the Log Activity tab, create a report to make use of the existing saved search.
Answer: B
NEW QUESTION 17
An analyst wants to analyze the long-term trending of data from a search.
Which chart would be used to display this data on a dashboard?
- A. Pie Chart
- B. Scatter Chart
- C. Bar Graph
- D. Time Series chart
Answer: D
Explanation:
Explanation
Time series charts are graphical representations of your activity over time.
Peaks and valleys that are displayed in the charts depict high and low volume activity. Time series charts are useful for short-term and long term trending of data.
https://www.ibm.com/docs/en/qsip/7.4?topic=management-time-series-chart-overview
NEW QUESTION 18
What steps are needed to add an Annotation to an event or flow that triggered a Rule?
- A. When creating a Rule, a custom Annotation can be automatically applied to events and flows that originate from specified Sources.
- B. When creating a Rule, a custom Annotation can be specified to automatically be applied to the event or flow that triggered the Rule.
- C. Annotations can be manually added to an Offense. These Annotations are then automatically applied to all events or flows which triggered the rule creating that Offense.
- D. Events and Flows cannot be Annotated, the only information allowed in an event or flow is data that was included in the original payload.
Answer: B
NEW QUESTION 19
An analyst is searching for a list of events that meet specific search criteria and wants to display only the source IP and destination IP information for the events.
To get the required information, the analyst can open the Log Activity tab and then:
- A. select the field names,
select the start and end time from the drop down fields in the filters section, then click search. - B. click add filter,
select the desired parameters, operators, values and field names,
then click search. - C. select search,
then new search,
scroll down and select time range, column definitions, the search parameters then click search. - D. select advanced search.
type the corresponding AQL query,
then click search.
Answer: A
NEW QUESTION 20
When an Offense is triggered, it only shows the events that triggered the Offense. The analyst wants to investigate further to see more events around the incident, not only those that triggered the Offense. The analyst clicks on the event count and sees the events belonging to the Offense.
How can the analyst processed to see a more detailed picture of what occurred?
- A. Right-click on the source IP, and choose View in DSM Editor.
- B. Right-click on the source IP, and choose More Options, then Information, and then Search Events
- C. Right-click and filter on the Destination IP.
- D. Right-click on the destination IP, and choose More Options, then Raw Events.
Answer: A
NEW QUESTION 21
From which tab in QRadar SIEM can an analyst search vulnerability data and remediate vulnerabilities?
- A. Admin
- B. Assets
- C. Log Activity
- D. Dashboard
Answer: C
NEW QUESTION 22
An analyst is reviewing a rule that is configured to create an Offense indexed by a uri domain name. But even after validating all the rule conditions, an Offense is not generated.
What could be the reason for this kind of behaviour?
- A. Normalized property Source IP is empty in the events.
- B. Custom property url domain name is empty in the events.
- C. Normalized property url domain name is empty in the events.
- D. Custom property Eventname is empty in the events.
Answer: D
NEW QUESTION 23
What does the Assets tab provide?
A unified view of the information that is kwon about:
- A. triggered Offenses.
- B. log sources.
- C. events and flows.
- D. network devices.
Answer: C
Explanation:
Explanation
https://www.ibm.com/docs/en/qradar-on-cloud?topic=administration-asset-management
NEW QUESTION 24
What is the reason for this system notification?
"Time synchronization to primary or Console has failed"
- A. Deny ntpdate communication on port 223.
- B. Deny ntpdate communication on port 423.
- C. Deny ntpdate communication on port 323.
- D. Deny ntpdate communication on port 123
Answer: D
Explanation:
Explanation
https://www.ibm.com/docs/en/qradar-on-cloud?topic=appliances-time-synchronization-failed The managed host cannot synchronize with the console or the secondary HA appliance cannot synchronize with the primary appliance.
Administrators must allow ntpdate communication on port 123. When time synchronization is incorrect, data might not be reported correctly to the console. The longer the systems go without synchronization, the higher the risk that a search for data, report, or offense might return an incorrect result. Time synchronization is critical to successful requests from managed host and appliances
NEW QUESTION 25
......
IBM Exam Practice Test To Gain Brilliante Result: https://www.testsdumps.com/C1000-018_real-exam-dumps.html
